Welcome to Code Forum!

Join a community that supports you and your coding journey from day one. We strive to be a friendly, supportive community that empowers everyone to be better developers. By registering with us, you'll be able to discuss, share and private message with other members of our community.

SignUp Now!
  • Guest, before posting your code please take these rules into consideration:
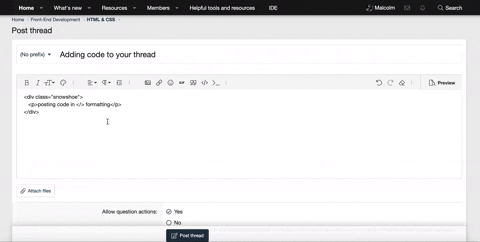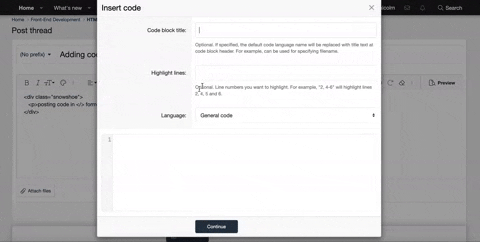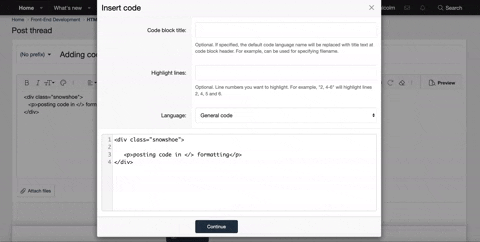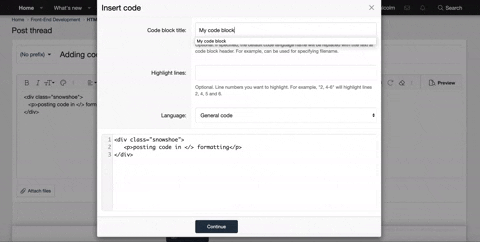
    • It is required to use our BBCode feature to display your code. While within the editor click < / > or >_ and place your code within the BB Code prompt. This helps others with finding a solution by making it easier to read and easier to copy.
    • You can also use markdown to share your code. When using markdown your code will be automatically converted to BBCode. For help with markdown check out the markdown guide.
    • Don't share a wall of code. All we want is the problem area, the code related to your issue.

    GIF shows where to locate </> in the thread and or post editor toolbar.
    To learn more about how to use our BBCode feature, review our "How to post your code into threads" here.

    Thank you, Code Forum.

JavaScript Creating HTML elements using JavaScript and using innerHTML (Security)

Malcolm

Administrator
Administrator
Staff Team
Code+
Hi everyone,

I'm trying to create a new HTML in JavaScript using createElement function and I want to add content within that element. The easiest way to do this, is using createdElement.innerHTML = "content";. However, I've been seeing a couple resources where using innerHTMl is a potential security risk. What I don't know is in what context is it a security risk. Is it just a security risk in general or is it security risk when it is used in particular way?

For example, would this be considered 'safe'?
JavaScript:
var result = document.getElementById("result");
var createPTag = document.createElement("p");
createPTag.innerHTML = "Testing";
result.appendChild(createPTag);
 
Hey there.

The code you have is completely safe. It's when you're using innerHTML to insert text that you have no control over (e.g. user-input text) that it becomes a risk. In this case, and perhaps most cases, it would be better to use the textContent property.

I remember a while back there was this chat room I and a few others were on, and it used innerHTML when adding new messages, so a few of the users exploited it by sending messages such as <img src="a" onerror="alert('some message or other script')">. In this case it was a security risk because the content inserted into the page with innerHTML was supplied by users.
 

Buy us a coffee!

Buy me a coffee.
Back
Top Bottom