Welcome to Code Forum!

Join a community that supports you and your coding journey from day one. We strive to be a friendly, supportive community that empowers everyone to be better developers. By registering with us, you'll be able to discuss, share and private message with other members of our community.

SignUp Now!
  • Guest, before posting your code please take these rules into consideration:
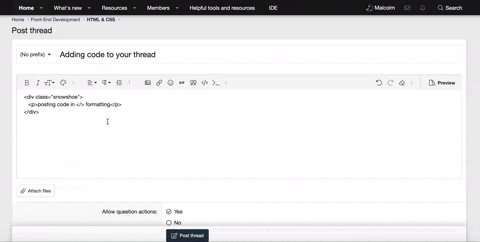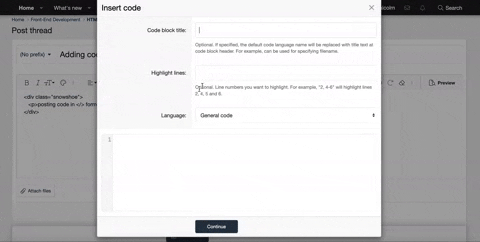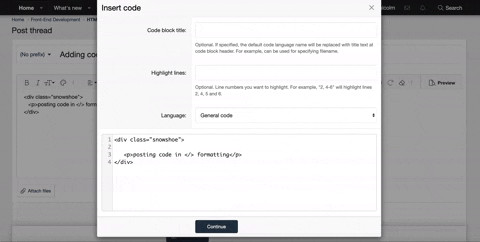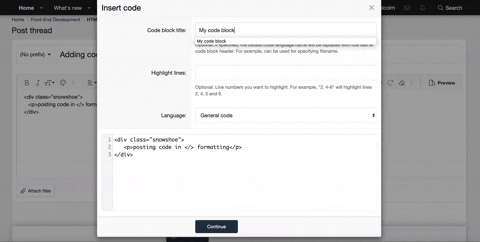
    • It is required to use our BBCode feature to display your code. While within the editor click < / > or >_ and place your code within the BB Code prompt. This helps others with finding a solution by making it easier to read and easier to copy.
    • You can also use markdown to share your code. When using markdown your code will be automatically converted to BBCode. For help with markdown check out the markdown guide.
    • Don't share a wall of code. All we want is the problem area, the code related to your issue.

    GIF shows where to locate </> in the thread and or post editor toolbar.
    To learn more about how to use our BBCode feature, review our "How to post your code into threads" here.

    Thank you, Code Forum.

Display contact info, but protect against spam

amd.64

Coder
I am new to the forums, and although I have done web design in HTML, Java Script and CGI it has been awhile, about 20 years in fact. I have done very little with CSS. Please bear with me as I will likely have several questions. I do have extensive experience with Visual Basic, I have had Java and C# classes but that is where it ended. So I at least have the foundations for scripting and programming.

Back when I last designed a website to protect email against spam I simply just created a form. At least for the site I designed phone spam wasn't an issue.

What is the best way in todays world wide web to protect against both email and phone spam. I would like both to be a simple click. Is an email form still the best way to protect email? What is the best way to protect against phone spam?

Thank You

Hey there,
So, this is a "double edge sword" concept. On the one hand, reducing the amount of spam is possible, on the other hand, completely avoiding it is well, unavoidable unless you remove contact info. Best ways to avoid mass spam campaigns are to avoid using the 'tel' command for phone numbers, and avoid using 'mailto' command on emails.

What you can do is create a button for emails and in the backend capture user input from the form and send off the email, without the need for the 'mailto' command. You can also do the same thing for the 'tel' command... just have the user click the button and in the backend run that as a 'tel' command. This would help reduce the risk of email/phone harvesting bots for spam campaigns.
 
So just having an email address or phone number on a website does not mean they will be found by bots? They actually have to be links with mailto or tel on them?
Typically, when email/phone harvester bots are written, they are written in a way that will look for the typical email format ([email protected].. etc) (+1115555555, 111-555-5555, (111)555-5555... )... the phone formats will be by country of course. They will also look for any links that have the tel/mailto commands in the src attribute like so:
HTML:
<a src="tel:+1115555555">Call Us</a>
<a src="mailto:[email protected]">Email Us</a>
Point being: email/phone harvesting will never be fully unavoidable. Best practices are to attempt to bypass the search by a bit of obfuscation...rather than to use the @ for an email you can do "abc(at)abc.com", rather than using .domain, you could use the same technique and do "abc(at)abc(dot)com", or something to that extent. For phone numbers, one potential technique is to use spaces to separate the grouped numbers like "111 111 5555". Again, not the "silver bullet", but at least it helps reduce the amount of spam if you really need email/phone on your site
 
Last edited:
I am thinking something along these lines. The code works as intended. However I prefer not to have the script where I want the mailto link.

I would rather have the script in the head and then called from where I want the link. Problem is, as I said before I have a heard time with getting Javascript and HTML to play nice. Also will this actually do anything to prevent spam? I am an experienced network / systems administrator and understand what @Antero360 is saying about it is impossible to remove all threats. I seen some comment in another forum about not to worry about it and just use a good spam filter, but the way I look at it is why temp fate.

If this will actually work the way I would like then I will duplicate it, then change the code for email to code for phone.

Code:
<!doctype html>
<html>
<body>
  <script>
    const recipient = "john";
    const domain = "example";
    const tolevel = "us"
    
    email = recipient + "@" + domain + "." + tolevel;
    maillink = "mailto:" + email

    // create link dynamically
    var link = document.createElement('a');

    // set href attribute
    link.href = maillink;

    // set link text
    link.text = email;

    // append link element to the body
    document.body.appendChild(link);

  </script>
</body>
</html>

All that said are there any good, easy to understand / follow online courses (preferably free as funds are currently non-existent)?

Thank you
 
I am thinking something along these lines. The code works as intended. However I prefer not to have the script where I want the mailto link.

I would rather have the script in the head and then called from where I want the link. Problem is, as I said before I have a heard time with getting Javascript and HTML to play nice. Also will this actually do anything to prevent spam? I am an experienced network / systems administrator and understand what @Antero360 is saying about it is impossible to remove all threats. I seen some comment in another forum about not to worry about it and just use a good spam filter, but the way I look at it is why temp fate.

If this will actually work the way I would like then I will duplicate it, then change the code for email to code for phone.

Code:
<!doctype html>
<html>
<body>
  <script>
    const recipient = "john";
    const domain = "example";
    const tolevel = "us"
  
    email = recipient + "@" + domain + "." + tolevel;
    maillink = "mailto:" + email

    // create link dynamically
    var link = document.createElement('a');

    // set href attribute
    link.href = maillink;

    // set link text
    link.text = email;

    // append link element to the body
    document.body.appendChild(link);

  </script>
</body>
</html>

All that said are there any good, easy to understand / follow online courses (preferably free as funds are currently non-existent)?

Thank you
So given you are an experienced sysadmin, you should already know that email spam campaigns are near impossible to prevent... the only true way to really stop them...is to not have any emails on your form. If you have a good email service, then you should be alright. Reputable email services, like outlook, gmail, do a pretty good job with their default spam filtering... also knowing how to set up filters based on whatever gets through helps as well. But to reiterate the point: email harvesting is not something that can easily be prevented in totality... also, I wouldn't consider it "tempting fate", but rather "learning from experience" 🙂
 
So given you are an experienced sysadmin, you should already know that email spam campaigns are near impossible to prevent... the only true way to really stop them...is to not have any emails on your form. If you have a good email service, then you should be alright. Reputable email services, like outlook, gmail, do a pretty good job with their default spam filtering... also knowing how to set up filters based on whatever gets through helps as well. But to reiterate the point: email harvesting is not something that can easily be prevented in totality... also, I wouldn't consider it "tempting fate", but rather "learning from experience" 🙂

I am not nor have I ever tried to prevent it security issues / breaches 100%, because I know it can't be done. Just as I know that I cannot 100% prevent getting in an automobile accident, I can mitigate the chances by not speeding, driving drunk or drive at night with no lights. No doing so doesn't 100% guarantee that I won't get in an accident, it does however reduce the chances.

Just as I know that there is still a chance of getting in an automobile accident I know that i will inevitably get spam. I have my own Exchange server with Microsoft's antispam filters for Exchange configured. I had an external spam filter until recently when the one I had stop offering that service and have not yet found a new one. (I am still looking for one I like). Exchange has been doing a good job of filtering out spam lately, but why give it more work that isn't necessary (which what I meant by my comment "why tempt fate"). As a network / system admin security is #1 with me. However, part of the reason of having a website is to get contact information to people who are looking for you (me), other wise a website, in this instance is useless. So I have to put my contact information slightly at risk, but if there is a way to mitigate that risk, even a little bit, then why wouldn't one take it. It is called a layered approach, hide contact info from bots, while still displaying it to website visitors as well has have one or more spam filters.
Again, as a sysadmin, you have plenty of tools at your disposal that are already effective enough as they are. Ever heard of the saying: Don't overthink it? As I have previously mentioned, you can only do so much to mitigate it: changing .com to (dot)com, name@ to name(at)domain(dot)com.. these give you a pretty good chance of not getting hit, for as long as the gremlins don't add these methods to their search algos in their bots... another thing you can try: try to detect whether user really is a user before loading in any contact info: cross reference ip address with established blacklists and known spam ips.. even with that method, you're still not 100%... something else you can try: completely obfuscating your contact info in a "challenge-like" format... aka base64 encode and ask users to decode, but at that point, you'll be losing potential clients over insignificant worries..I have seen this approach in the wild, and let me be as blunt as possible: this approach comes off as arrogant and not worth the time nor the effort to attempt: not everyone is as tech savvy as either you or myself. Other than that, if you are really that worried about it, then just don't put any info on there, it will get scrapped, only a matter of time. You already have a pretty good system of handling spam emails from what you are sharing... leave it as it be and to reiterate the commentary from the other forum: don't worry about it too much... that is actually the least of your problems. Invest your time, your energy, and your sanity into fortifying your site from XSS, SQLi, directory traversal, bruteforcing, file uploading, rce, you know, all the good stuffs. I'll be more than happy to provide a pen-test for you if you want go down that path.

My best advice as both a web/software dev, and cybersec hobbiest: don't go insane attempting to go full secure or near full secure: no one ever has, no one ever will.
 

Buy us a coffee!

Buy me a coffee.
Back
Top Bottom