Welcome to Code Forum!

Join a community that supports you and your coding journey from day one. We strive to be a friendly, supportive community that empowers everyone to be better developers. By registering with us, you'll be able to discuss, share and private message with other members of our community.

SignUp Now!
  • Guest, before posting your code please take these rules into consideration:
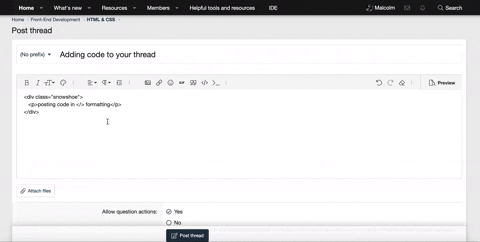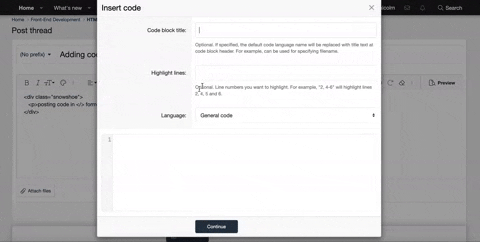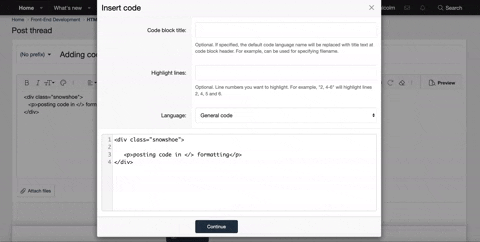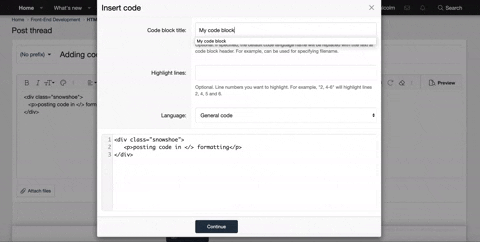
    • It is required to use our BBCode feature to display your code. While within the editor click < / > or >_ and place your code within the BB Code prompt. This helps others with finding a solution by making it easier to read and easier to copy.
    • You can also use markdown to share your code. When using markdown your code will be automatically converted to BBCode. For help with markdown check out the markdown guide.
    • Don't share a wall of code. All we want is the problem area, the code related to your issue.

    GIF shows where to locate </> in the thread and or post editor toolbar.
    To learn more about how to use our BBCode feature, review our "How to post your code into threads" here.

    Thank you, Code Forum.

Answered Is this code malicious?

Chacharo9

New Coder
I need some help. Is the following code malicious in any way?

While trying to download a pdf, I came upon the following code from this website: https://codingcat.codes/2019/01/09/download-view-protected-pdf-google-drive-js-code/

JavaScript:
let jspdf = document.createElement("script");
 
jspdf.onload = function () {
 
    let pdf = new jsPDF();
    let elements = document.getElementsByTagName("img");
    for (let i in elements) {
        let img = elements;
        console.log("add img ", img);
        if (!/^blob:/.test(img.src)) {
            console.log("invalid src");
            continue;
        }
        let can = document.createElement('canvas');
        let con = can.getContext("2d");
        can.width = img.width;
        can.height = img.height;
        con.drawImage(img, 0, 0, img.width, img.height);
        let imgData = can.toDataURL("image/jpeg", 1.0);
        pdf.addImage(imgData, 'JPEG', 0, 0);
        pdf.addPage();
    }
 
    pdf.save("download.pdf");
};
 
jspdf.src = '<a class="vglnk" href="https://cdnjs.cloudflare.com/ajax/libs/jspdf/1.5.3/jspdf.debug.js" rel="nofollow"><span>https</span><span>://</span><span>cdnjs</span><span>.</span><span>cloudflare</span><span>.</span><span>com</span><span>/</span><span>ajax</span><span>/</span><span>libs</span><span>/</span><span>jspdf</span><span>/</span><span>1</span><span>.</span><span>5</span><span>.</span><span>3</span><span>/</span><span>jspdf</span><span>.</span><span>debug</span><span>.</span><span>js</span></a>';
document.body.appendChild(jspdf);
 
Last edited by a moderator:
Solution
D
Why exactly do you suspect this code to be possibly malicious ? Clearly it's just grabbing all images from the current page and putting them in a pdf file. Seems quite harmless to me. The link
https://cdnjs.cloudflare.com/ajax/libs/jspdf/1.5.3/jspdf.debug.js
also looks very legitimate. If you ran the code, and it did not not give you any issues (or so I assume from what you write) why are you worried about it ?
The final link is weird though, putting every element of the url in its own <span>. Quite a silly thing to do, but no harm done.
Why exactly do you suspect this code to be possibly malicious ? Clearly it's just grabbing all images from the current page and putting them in a pdf file. Seems quite harmless to me. The link
https://cdnjs.cloudflare.com/ajax/libs/jspdf/1.5.3/jspdf.debug.js
also looks very legitimate. If you ran the code, and it did not not give you any issues (or so I assume from what you write) why are you worried about it ?
The final link is weird though, putting every element of the url in its own <span>. Quite a silly thing to do, but no harm done.
 
Solution
@cbreemer Hey there. Thank you for taking a look at the code.

The final link is what worried me since it was written in a manner that seemed quite strange.

Once again, thank you for taking a look and double checking for me. You're awesome!
 
Glad I could help. Yes, that was weirdly written. Not the link itself, but the way the url was put on the screen. I've never seem something like that. Probably generated code. But absolutely harmless.
 
Hey there,

I believe I may have someone who may be able to determine this, @Antero360 any idea if this code is malicious or not?
Just seen this today lol. @Chacharo9 the code is completely harmless. All it's doing is creating a script tag in the DOM and adding the javascript that pulls images from the given link and saves them into a pdf. Now, if that code was minimized, then there could be a potential, but minified javascript is standard, so no need to worry there too much.. unless the code itself was obfuscated in such a way that function/variable names had hex values in them.
 
Just seen this today lol. @Chacharo9 the code is completely harmless. All it's doing is creating a script tag in the DOM and adding the javascript that pulls images from the given link and saves them into a pdf. Now, if that code was minimized, then there could be a potential, but minified javascript is standard, so no need to worry there too much.. unless the code itself was obfuscated in such a way that function/variable names had hex values in them.
@Antero360 Thank you for taking a second look. This makes me feel much better. I was very worried about it. That's what I get for running a code on the Google Chrome console without first looking at it in detail.
 

Buy us a coffee!

Buy me a coffee.
Back
Top Bottom