Welcome to Code Forum!

Join a community that supports you and your coding journey from day one. We strive to be a friendly, supportive community that empowers everyone to be better developers. By registering with us, you'll be able to discuss, share and private message with other members of our community.

SignUp Now!
  • Guest, before posting your code please take these rules into consideration:
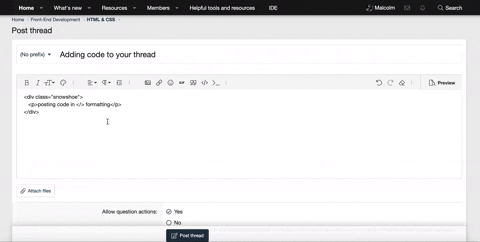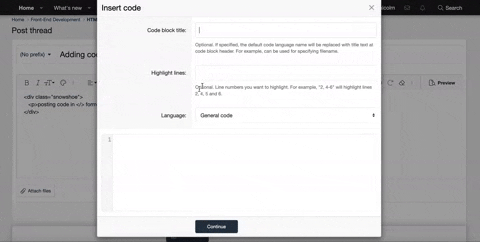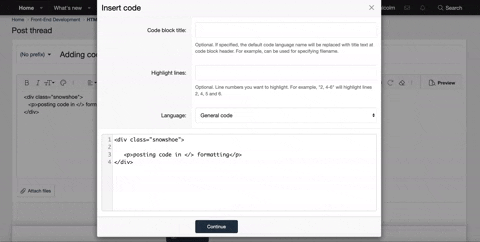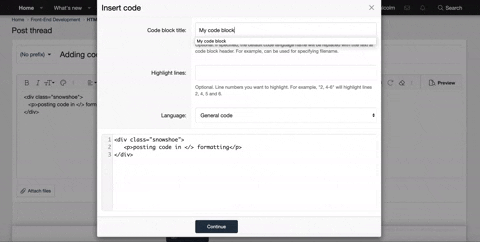
    • It is required to use our BBCode feature to display your code. While within the editor click < / > or >_ and place your code within the BB Code prompt. This helps others with finding a solution by making it easier to read and easier to copy.
    • You can also use markdown to share your code. When using markdown your code will be automatically converted to BBCode. For help with markdown check out the markdown guide.
    • Don't share a wall of code. All we want is the problem area, the code related to your issue.

    GIF shows where to locate </> in the thread and or post editor toolbar.
    To learn more about how to use our BBCode feature, review our "How to post your code into threads" here.

    Thank you, Code Forum.

PHP submit button sends to blank page loginback??

220061

Well-Known Coder
Hello, I don't really know how to explain this but right now when I submit it stays on the loginback page andit gives me a blank screen? why is it doing this? I have already tried to display the error messages by using
ini_set('display_errors', 1);
ini_set('display_startup_errors', 1);
error_reporting(E_ALL);
but it doesn't tell me anything?

code:
PHP:
<?php
// dit is allemaal nog niet veilig
session_start();
// Check if the user is already logged in, if yes then redirect him to welcome page
if(isset($_POST["email"]) && $_POST["password"] === true){
    header("location: welcome.php");
    exit;
}
// Include config file
include "config.php";

$email = mysqli_real_escape_string($conn , $_POST['email']);
$password = mysqli_real_escape_string($conn , $_POST['password']);
$stmt = $conn->prepare("SELECT user_id, email, password FROM users WHERE email=? AND password=? LIMIT 1");
if ($stmt->num_rows === 1) {
    $row = $stmt->fetch_array(MYSQLI_ASSOC);
    if (!password_verify($password, $row['password'])) {
        // invalid = run set of functions
        echo "This is false";
        header( "refresh:5;url=login.php" );
    }
    else {
        // login
        if($stmt->num_rows == 1)  //To check if the row exists
            {
                if($stmt->fetch()) //fetching the contents of the row
                {
                  
                    //    $_SESSION['Logged'] = 1;
                       $_SESSION['user_id'] = $user_id;
                       $_SESSION['username'] = $username;
                       echo 'Success!';
                       header("Location: welcome.php");
                 }
    
            
                else {
                    echo "INVALID USERNAME/PASSWORD Combination! You will be send back in 5 seconds 1";
                    header( "refresh:5;url=login.php" );
                }
                $stmt->close();
        }else{   
            echo "INVALID USERNAME/PASSWORD Combination! You will be send back in 5 seconds 2";
            header( "refresh:5;url=login.php" );
        }
    }
}
$stmt->bind_param('ss', $email, $password);
$stmt->execute();
$stmt->bind_result($user_id, $email, $password);
$stmt->store_result();


$conn->close();
?>
 
UPDATE still doesn't work but this is the code right now it stops working by the password verify. thats when it continues to give me false

PHP:
<?php
// dit is allemaal nog niet veilig
session_start();
// Check if the user is already logged in, if yes then redirect him to welcome page
if(isset($_POST["email"]) && $_POST["password"] === true){
    header("location: welcome.php");
    exit;
}
// Include config file
include "config.php";

// $id = mysqli_real_escape_string($conn, $_GET['ID']);
$email = mysqli_real_escape_string($conn , $_POST['email']);
$password = mysqli_real_escape_string($conn , $_POST['password']);

$sql = "SELECT email, password FROM users WHERE email=?";
$stmt = $conn->prepare($sql);
mysqli_report(MYSQLI_REPORT_STRICT);

if ($stmt = $conn->prepare($sql)) {
    $stmt->bind_param('s', $email);
    $stmt->execute();
    $stmt->bind_result($email, $password);
    // $stmt->store_result();
    $row = $stmt->fetch();
    // $resultSet = $stmt->get_result();
    // $rows = $resultSet->fetchAll(MYSQLI_ASSOC);
    // foreach ($rows as $row) {
    //     printf("%s (%s)\n", $row["email"], $row["password"]);
    // }
  
    //oke hij gaat hier nu veder
    if (password_verify($password, $row['password'])) {
                // login
                if($stmt->num_rows > 0)  //To check if the row exists
                {
                    if($stmt->fetch()) //fetching the contents of the row
                    {
                    
                        //    $_SESSION['Logged'] = 1;
                           $_SESSION['user_id'] = $user_id;
                           $_SESSION['username'] = $username;
                           echo 'Success!';
                           header("Location: welcome.php");
                     }
      
              
                    else {
                        echo "INVALID USERNAME/PASSWORD Combination! You will be send back in 5 seconds 1";
                        header( "refresh:5;url=login.php" );
                    }
                    $stmt->close();
            }else{ 
                echo "INVALID USERNAME/PASSWORD Combination! You will be send back in 5 seconds 2";
                header( "refresh:5;url=login.php" );
            }
    }
    else {
        echo "This is false";
        var_dump($email); // results null
        var_dump($password);//results to null
        // header( "refresh:5;url=login.php" );
    }

// $stmt->bind_param('ss', $email, $password);
// $stmt->execute();
// $stmt->bind_result($user_id, $email, $password);
// $stmt->store_result();


$conn->close();
}else{
    echo "it doesnt work";
}
?>
 
new update still doesn't work its stuck on if ($stmt->num_rows == 1){

PHP:
<?php
// dit is allemaal nog niet veilig
session_start();
// Check if the user is already logged in, if yes then redirect him to welcome page
if(isset($_POST["email"]) && $_POST["password"] === true){
    header("location: welcome.php");
    exit;
}
// Include config file
include "config.php";

// $id = mysqli_real_escape_string($conn, $_GET['ID']);
// $email = mysqli_real_escape_string($conn , $_POST['email']);
// $password = mysqli_real_escape_string($conn , $_POST['password']);
$email = $_POST['email'];
$password = $_POST['password'];

$sql = "SELECT email, password FROM users WHERE email=?";
$stmt = $conn->prepare($sql);
mysqli_report(MYSQLI_REPORT_STRICT);

if ($stmt = $conn->prepare($sql)) {
    $stmt->bind_param('s', $email);
    $stmt->execute();
    $stmt->bind_result($email, $password);
    $row = $stmt->get_result()->fetch_assoc();
    $result= mysqli_query($conn,$sql);
    // $stmt->store_result();
    //$row = $stmt->fetch();
    // $resultSet = $stmt->get_result();
    // $rows = $resultSet->fetchAll(MYSQLI_ASSOC);
    // foreach ($rows as $row) {
    //     printf("%s (%s)\n", $row["email"], $row["password"]);
    // }
    echo "<br>";
   
    //oke hij gaat hier nu veder
    var_dump($password); // dit is nu de code van de db?
    $test = $row['password'];
    var_dump($test); // dit is null
    var_dump($result);
    if (password_verify($password, $row['password'])) {
                // login
                if($stmt->num_rows == 1)  //To check if the row exists
                {
                    if($stmt->fetch()) //fetching the contents of the row
                    {
                     
                        //    $_SESSION['Logged'] = 1;
                           $_SESSION['user_id'] = $user_id;
                           $_SESSION['username'] = $username;
                           echo 'Success!';
                           header("Location: welcome.php");
                     }
       
               
                    else {
                        echo "INVALID USERNAME/PASSWORD Combination! You will be send back in 5 seconds 1";
                        // header( "refresh:5;url=login.php" );
                    }
                    $stmt->close();
                }else{  
                    echo "INVALID USERNAME/PASSWORD Combination! You will be send back in 5 seconds 2";
                    // header( "refresh:5;url=login.php" );
                }
    }
    else {
        echo "This is false";
        // header( "refresh:5;url=login.php" );
    }

// $stmt->bind_param('ss', $email, $password);
// $stmt->execute();
// $stmt->bind_result($user_id, $email, $password);
// $stmt->store_result();


$conn->close();
}else{
    echo "it doesnt work";
}
?>
 

Buy us a coffee!

Buy me a coffee.
Back
Top Bottom